Showing posts with label BlackAss technical bangla Top 10 Hacking Tools Which programming languages are useful for hacking রসায়নের কিছু মজার তথ্য. Show all posts

Tuesday, September 12, 2017

রসায়নের কিছু মজার তথ্য

রসায়ন অনেকের কাছে সহজবোধ্য না হলেও এটি কিন্তু যথেস্ট মজার একটি বিষয়। রসায়ন মানেই অনেক মজা। এর আগে রসায়নের বেশ কিছু মজার বিষয় নিয়ে পোস্ট করেছি। যথারীতি আজকেও থাকছে রসায়নের কিছু মজা। চলুন দেখি আজকের মজাগুলো কি!
১. আপনি যদি এক গ্লাস পানিতে এক মুঠো লবন দেন তাহলে তো গ্লাসের পানি পরে যাবে ,তাই না ? দিয়ে দেখুন তো পরে কি না । কি অবাক হচ্চেন , পানির উচ্চতা আরও কমে গেল , তাই না ?
২. আপনার শরীরে যে পরিমান কার্বন আছে তা দিয়ে ৯০০০ পেন্সিল বানানো যাবে !!!
৩. সোনা অনেক দুর্লভ। দাম তো আকাশচুম্বী। কিন্তু আপনি কি জানেন, পৃথিবীতে যে পরিমান সোনা আছে তা দিয়ে সম্পূর্ণ পৃথিবী ঢেকে দিলে হাঁটু পরিমান উচ্চতা হবে।
৪. অক্সিজেন গ্যাস এর কোন বর্ণ নাই, কিন্তু তরল ও কঠিন অক্সিজেন নীল বর্ণের।
৫. হাইড্রফ্লুরিক এসিড এতবেশি ক্ষয়কারী যে গ্লাস গলিয়ে (dissolve ) ফেলে, কিন্তু তারপরেও এটাকে দুর্বল এসিড বলা হয় ।
৬. পৃথিবীর সবচে দুর্লভ মৌল এস্তেতিন, সারা পৃথিবীতে মাত্র ২৮ গ্রাম এস্তেতিন আছে।
৭. বায়ুমণ্ডলের প্রায় ২০ % অক্সিজেন শুধুমাত্র আমাজন রেইন ফরেস্টের মাধ্যমেই উৎপন্ন হয় ।
৮. সাধারন তাপমাত্রায় ব্রোমিন ও পারদ এ দুটো মৌল ই তরল ।
৯. আমরা জানি পানির রাসায়নিক নাম (H2O ) এইচ টু ও , কিন্তু ইউপ্যাক (IUPAC) অনুযায়ী পানির রাসায়নিক নাম ডাইহাইড্রজেন মনোঅক্সাইড।
১০. মহাবিশ্বে সবচেয়ে বেশি পাওয়া যায় হাইড্রোজেন কিন্তু পৃথিবীতে সবচে বেশি পাওয়া যায় অক্সিজেন (প্রায় ৪৯% বায়ুমণ্ডল+ ভুমি+সাগর)
১১. বজ্রপাতে প্রতিবছর অনেক লোক মারা যায়, কিন্তু আপনি কি জানেন বজ্রপাত না থাকলে পৃথিবীর প্রাণীকুল ধ্বংস হয়ে যেত।কারন বজ্রপাতের মাধ্যেমেই ওজোন তৈরি হয় ।
সবাই ভাল থাকবেন। হয়ত আর একদিন আরও মজার কিছু নিয়ে হাজির হব, কিন্তু আপনাদের ভাল না লাগলে আর লিখব না। ধন্যবাদ।

Top 10 Hacking Tools

top-10-hacking-tools

Top 10 Hacking Tools

Wireshark

Wireshark is an open source packet analyzer. It is used to troubleshoot networks, it provides quick and easy network analysis, Originally Wireshark was named Ethereal until May 2016 due to trademark issues.
Wireshark is cross-platform and will run on Linux, MacOS, and Windows it uses the Qt widget toolkit to implement its user interface, it also uses pcap to capture packets. There is also a terminal-based (non-GUI) version of Wireshark called TShark. Wireshark, and the other programs distributed with it such as TShark, are free software, released under the terms of the GNU General Public License.

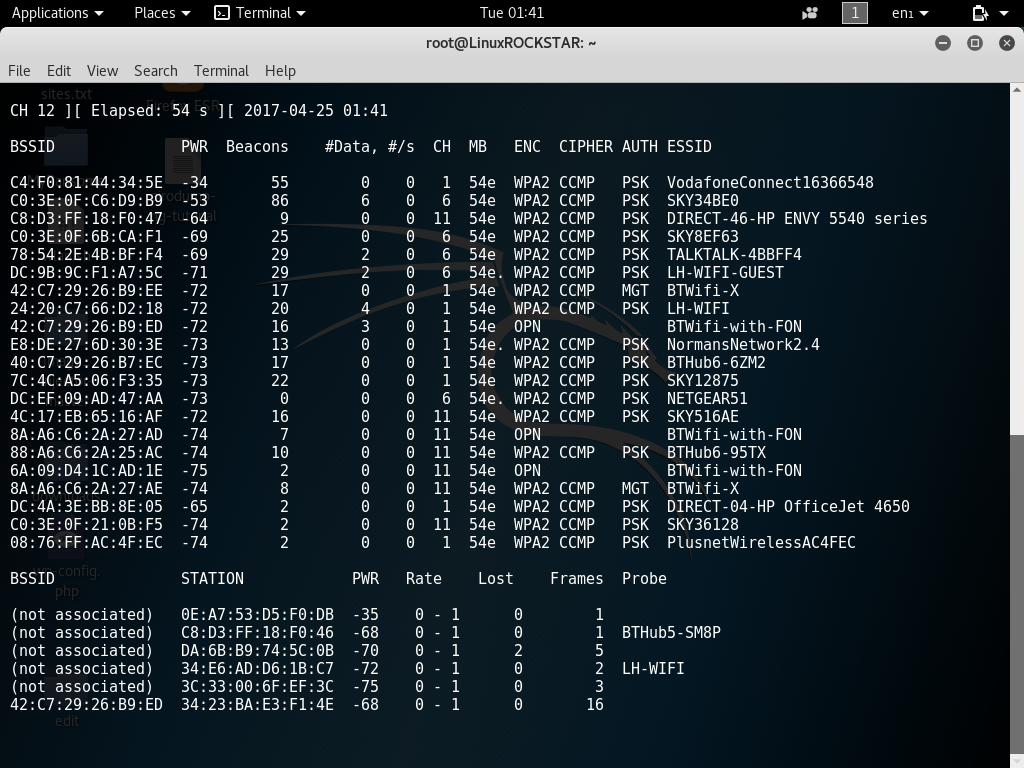
Airodump-ng

Airodump-ng is a Wi-Fi analysis tool used for packet capturing of raw 802.11 frames. It is particularly suitable for collecting WEP IVs (Initialization Vector) for the intent of using them with aircrack-ng. If you have a GPS receiver connected to the computer, airodump-ng is capable of logging the coordinates of the found access points.

Nmap

nmap
Nmap (Network Mapper) is a security vulnerability scanner, it was originally written by Gordon Lyon it can be used to discover hosts and services on computer networks. Nmap is excellent for creating maps of the network. Nmap sends specially crafted packets to the target host(s) and then analyzes their responses. It provides a lot of great features including probing networks and host discovery it can also detect operating systems and services. Nmap is excellent for vulnerability detection.

Reaver

Reaver is a tool designed to easily deploy brute force against WPS enabled wireless routers and access points, On average it takes Reaver around 4-10 hours to recover the target AP’s WPA/WPA2 pass phrase in plain text although generally it will most likely only take half this time to guess the correct WPS pin.
There are 100,000,000 Possible Key Values although the ending digit of the key value is known as a checksum witch is calculated based on the last 7 digits lowering the process down to 10,000,000 possibilities. WPS breaks the Pins/Keys in half during this process the keys are then broken down to 10,000 values for the first half and 1,000 for the second half of the key-chain this totals 11,000 possible pins to try lowing the overall time of this process drastically.

Social Engineering Toolkit (SET)

social-engineer-toolkit-set

The Social-Engineer Toolkit (SET) is specifically designed to perform advanced social engineering attacks against the human element of security. SET was designed to be released with the https://www.social-engineer.org launch and has quickly became a standard tool in a penetration testers arsenal. It comes default in various pen testing operating systems such as Kali Linux, Parrot OS, Black Arch.

WPScan

wpscan-kali-linux
WPScan is a black box WordPress vulnerability scanner that can be used to scan remote WordPress installations to find security issues.

Metasploit

Its best-known sub-project is the open source Metasploit Framework, a tool for developing and executing exploit code against a remote target machine. Other important sub-projects include the Opcode Database, shellcode archive and related research.

BeEF

beef-xss-2
BeEF is short for The Browser Exploitation Framework. It is a penetration testing tool that focuses on the web browser.
Amid growing concerns about web-borne attacks against clients, including mobile clients, BeEF allows the professional penetration tester to assess the actual security posture of a target environment by using client-side attack vectors. Unlike other security frameworks, BeEF looks past the hardened network perimeter and client system, and examines exportability within the context of the one open door: the web browser. BeEF will hook one or more web browsers and use them as beachheads for launching directed command modules and further attacks against the system from within the browser context.

PixieWPS

pixiewps-kali-linux
Pixiewps is a tool used for offline brute forcing of WPS pins, while exploiting the low or non-existing entropy of some wireless access points also known as the pixie dust attack, discovered by Dominique Bongard (slides and video). The pixiewps tool (developed by wiire), was born out of the Kali forums, and the development of the tool can be tracked throughout an interesting forum post.
In the correct environment, pixiewps dramatically speeds up the WPS brute force attack time from what was taking up to 12 hours to a a few seconds.

Hashcat

hashcat is the world’s fastest and most advanced password recovery utility, supporting five unique modes of attack for over 200 highly-optimized hashing algorithms. hashcat currently supports CPUs, GPUs, and other hardware accelerators on Linux, Windows, and OSX, and has facilities to help enable distributed password cracking.

Which programming languages are useful for hacking

Important Programming languages for Hackers

Many of our readers often send us queries about which programming language they should learn. Some want to know quick fix hacking solutions. Almost all tech gadgets are built with coding. Every App, game or site that you use is programmed in a particular computer language. You need to know that hacking is not a click-of-a-button job but a serialized and compartmentalized vocation which uses different programming languages for different uses.
Most of the websites out there will give you list of most popular programming languages in the world. We at Techworm try to make it more easy for budding security researchers and hackers by breaking up the programming languages used by hackers.
Hacking is usually meant to break a code. There are three sections of hacking ― Web Hacking, Exploit Writing & Reverse Engineering and each of it requires different programming language

1. Web Hacking

Since most of the tech is build around world wide web, it is important to learn web hacking to be a good hacker. Let’s say you are interested in hacking web apps and/or websites then you will need to learn web coding. Websites use mostly HTML, PHP and JavaScript so it is important to learn these three.

HTML:

One of the easiest and widely used static markup web language present in each and every website you see in your browser. It’s recommended to learn HTML because it helps understanding web actions, response, and logic.

JavaScript:

JS is a client-side web programming mostly used in web sites for better user interface and quick response. If you are interested in a hacking career you need to learn JavaScript because it helps to understand client-side mechanism which is essential for finding client-side flaws.

PHP:

A dynamic server-side language which is responsible for managing web-apps and database. PHP is considered one of the most essential language because it controls everything on site and server, like a captain of a ship. It is advised to learn PHP nicely.

SQL:

SQL is responsible for storing and managing sensitive and confidential data such as user credentials, bank and personal information about the website visitors. Black hat hackers mostly target SQL database and steal information which is later sold on underground dark web forum. If you want to be good security researcher, you should learn SQL so that you can find flaws in a website and report them.

2. Exploit Writing

After web hacking, another most important feature of hacking is exploits. You can crack a particular software by writing a exploit. But to write a exploit you need to learn either Python or Ruby.

Python:

It is said that a security researcher or hacker should know Python because it the core language for creating exploits and tools. Security experts and even pro hackers suggest that master Python is the best way to learn hacking. Python offers wider flexibility and you can create exploits only if you are good in Python.

Ruby:

Ruby is a simple yet complicated object-oriented language. Ruby is very useful when it comes to exploit writing. It is used for meterpreter scripting by hackers. The most famous hacker tool, Metasploit framework is programmed in Ruby. Though Ruby may not be as versatile as Python, knowledge of Ruby is must in understanding exploits.

3. Reverse Engineering

Reverse engineering, the process of taking a software program’s binary code and recreating it so as to trace it back to the original source code. If you know reverse engineering you can find flaws and bugs easily. If you want to learn reverse engineering you need to know C, C++ and Java. The process of converting the code written in high level language into a low level language without changing the original program is known as reverse engineering.
Do you think any other programming language is essential for wannabe hackers and security researchers? if yes then please comment below.